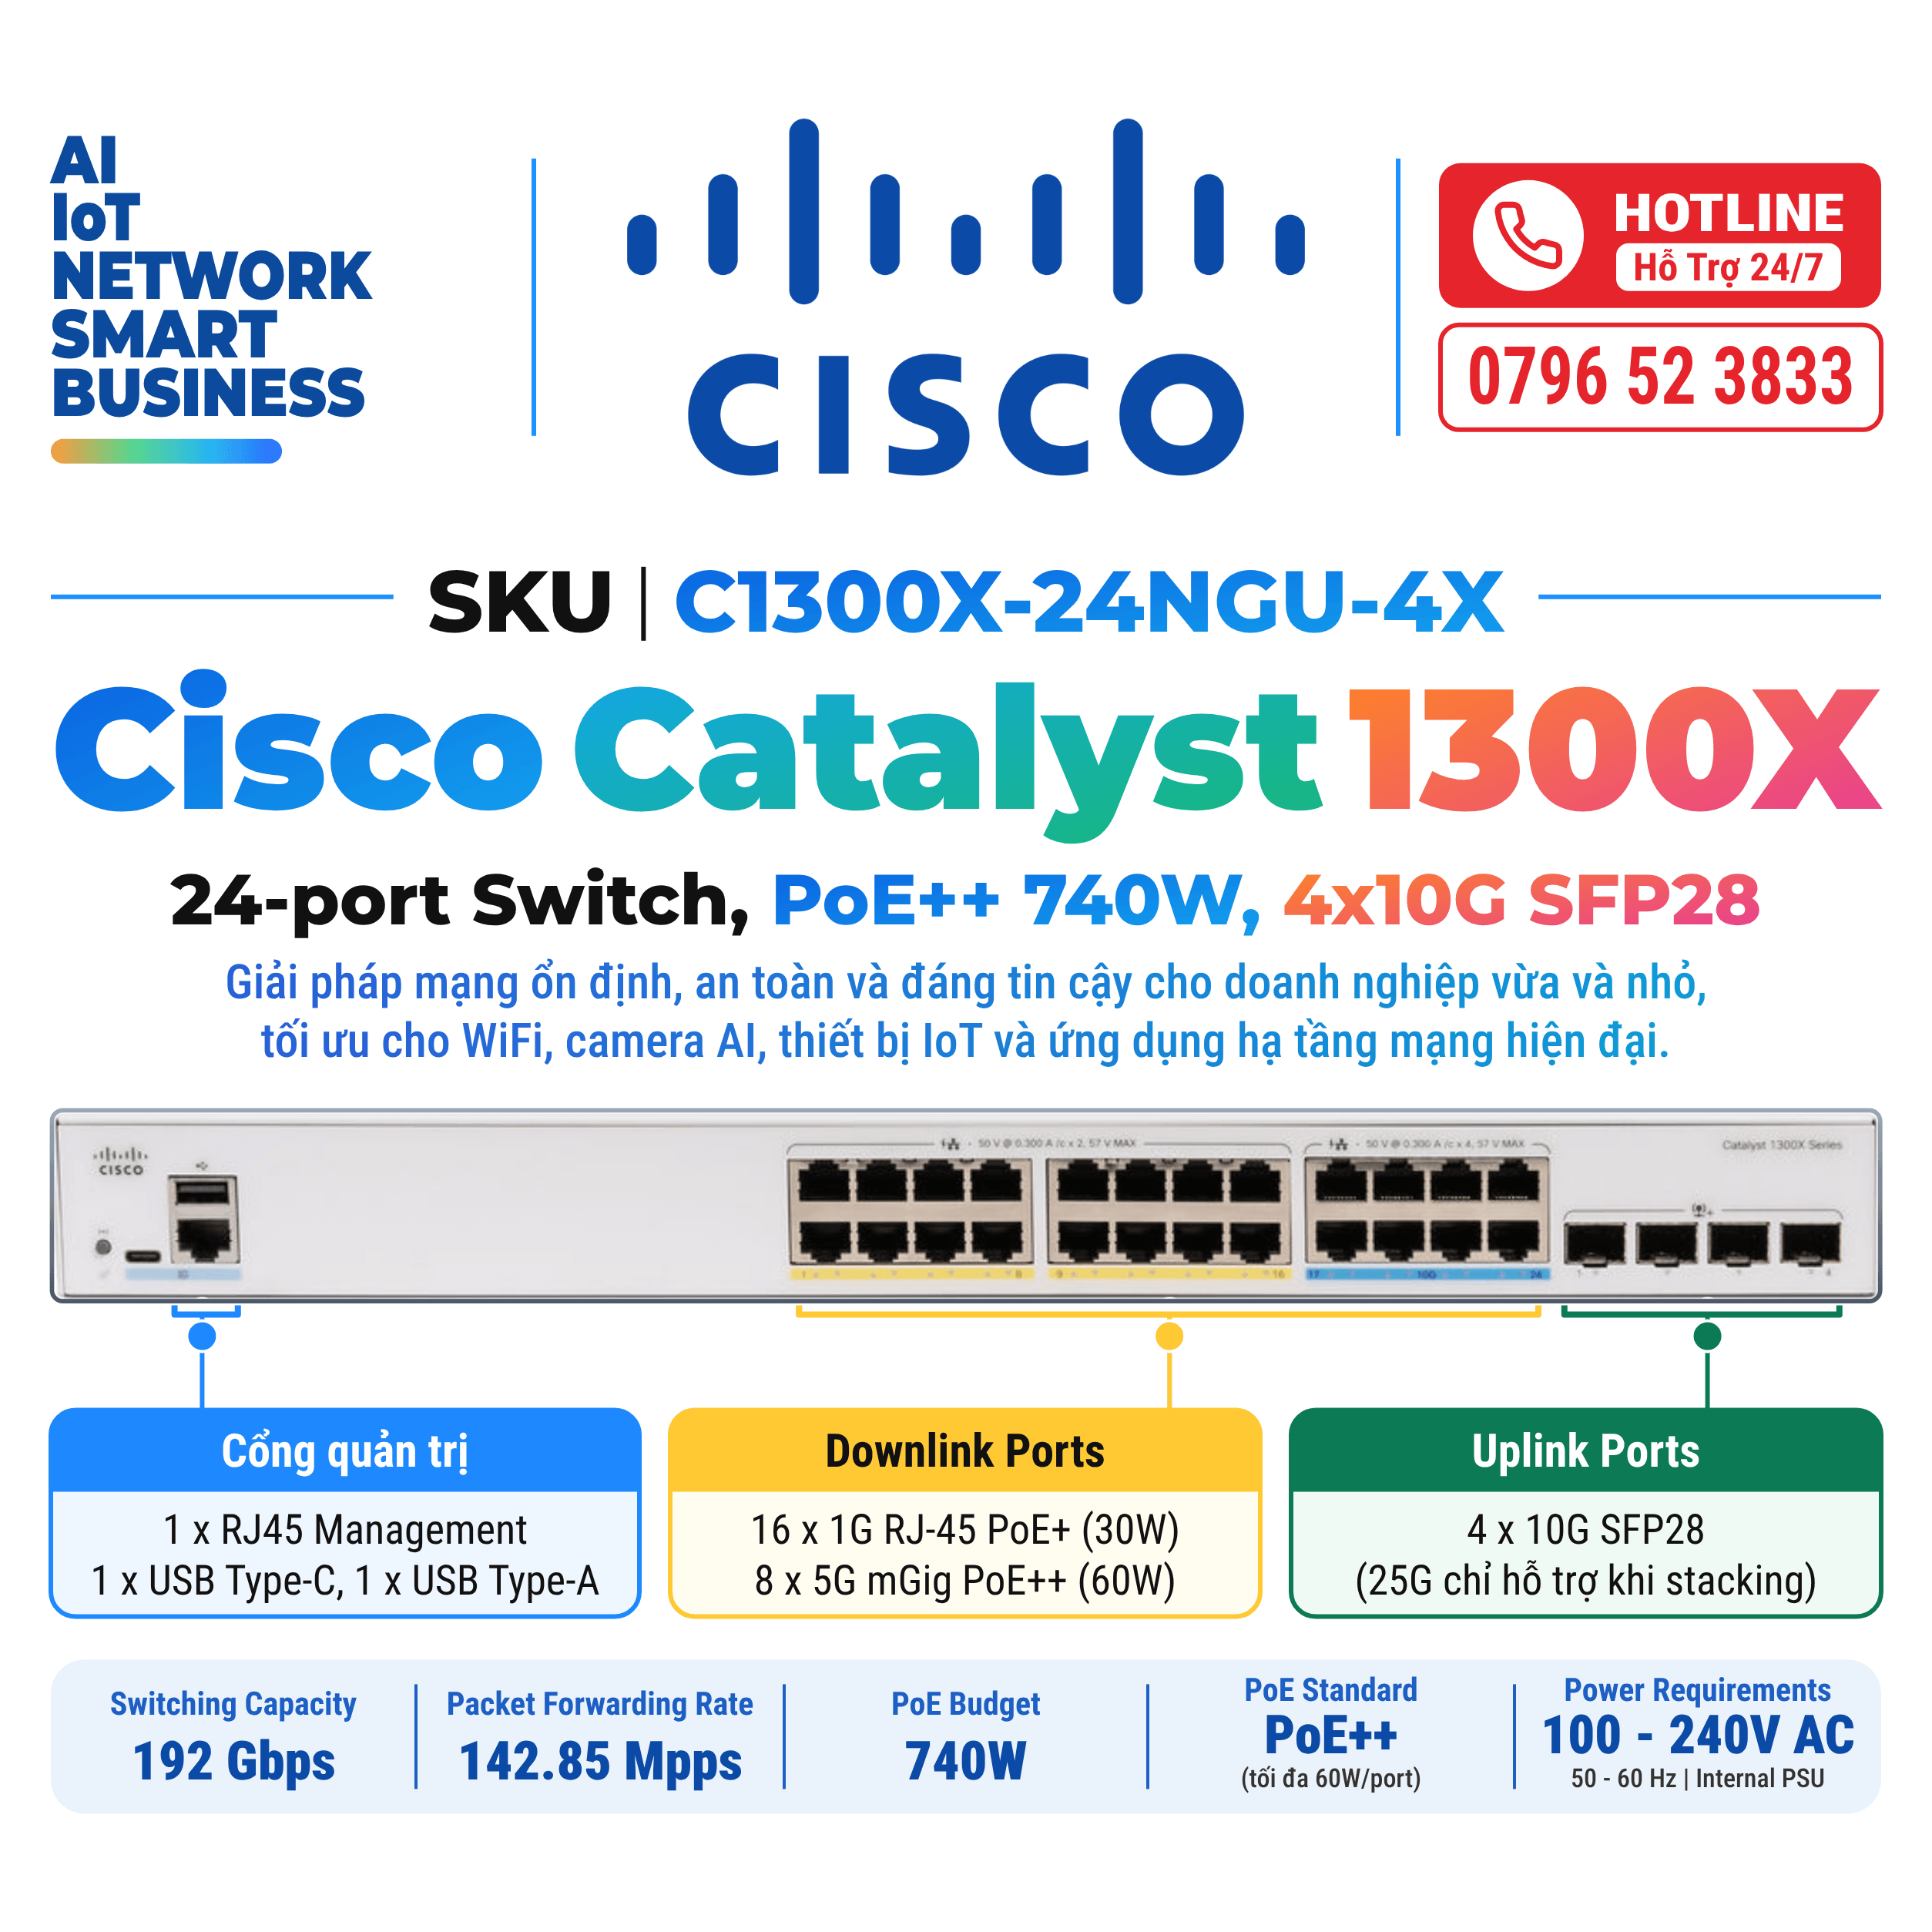
| Product specifications for the Cisco Catalyst C1300X-24NGU-4X |
| SKU |
C1300X-24NGU-4X |
| Product description |
Cisco Catalyst 1300 24-port Switch, 16x GE PoE+, 8x 5G PoE++, 4x10G SFP28, PoE budget 740W_C1300X-24NGU-4X |
| Performance |
Switching capacity and forwarding rate. All switches are wirespeed and nonblocking
● Switching capacity in gigabits per second (Gbps): 192
● Capacity in millions of packets per second (mpps) (64-byte packets): 142.85 |
| Layer 2 switching |
Spanning Tree Protocol (STP)
● Standard 802.1d spanning tree support
● Fast convergence using 802.1w (Rapid Spanning Tree [RSTP]), enabled by default Multiple Spanning Tree instances using 802.1s (MSTP); 16 instances are supported
● Per-VLAN Spanning Tree Plus (PVST+) and Rapid PVST+ (RPVST+); 126 instances are supported |
| Layer 2 switching |
Port grouping/link aggregation:
● Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP)
● Up to 8 groups
● Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link
aggregation |
| Layer 2 switching |
VLAN
● Support for up to 4094 VLANs (4078 – 4094 are for internal usage) simultaneously
● Port-based and 802.1Q tag-based VLANs, MAC-based VLAN, protocol-based VLAN, IP subnet-based VLAN
● Management VLAN
● Private VLAN with promiscuous, isolated, and community port
● Private VLAN Edge (PVE), also known as protected ports, with multiple uplinks Guest VLAN, unauthenticated VLAN
● Dynamic VLAN assignment via RADIUS server along with 802.1X client authentication
● Customer premises equipment (CPE) VLAN
● Auto surveillance VLAN (ASV) |
| Layer 2 switching |
Voice VLAN
Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices |
| Layer 2 switching |
Multicast TV VLAN
Multicast TV VLAN allows the single multicast VLAN to be shared in the network while subscribers remain in separate VLANs. This feature is also known as Multicast VLAN Registration (MVR) |
| Layer 2 switching |
VLAN translation
Support for VLAN one-to-one mapping, in which customer VLANs (C-VLANs) on an edge interface are mapped to service provider VLANs (S-VLANs), and the original C-VLAN tags are replaced by the specified S-VLAN |
| Layer 2 switching |
Q-in-Q
VLANs transparently cross a service provider network while isolating traffic among customers |
| Layer 2 switching |
Selective Q-in-Q
Selective Q-in-Q is an enhancement to the basic Q-in-Q feature and provides, per edge interface, multiple mappings of different C-VLANs to separate S-VLANs
Selective Q-in-Q also allows configuring of the Ethertype (Tag Protocol Identifier [TPID]) of the
S-VLAN tag Layer 2 protocol tunneling over Q-in-Q is also supported |
| Layer 2 switching |
Generic VLAN Registration Protocol (GVRP)/Generic Attribute Registration Protocol (GARP)
GVRP and GARP enable automatic propagation and configuration of VLANs in a bridged domain |
| Layer 2 switching |
Unidirectional Link
UDLD monitors physical connections to detect unidirectional links caused by incorrect |
| Layer 2 switching |
Detection (UDLD)
Wiring or cable/port faults to prevent forwarding loops and blackholing of traffic in switched networks |
| Layer 2 switching |
DHCP relay at Layer 2
Relay of DHCP traffic to a DHCP server in a different VLAN; works with DHCP Option 82 |
| Layer 2 switching |
Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping
● GMP limits bandwidth-intensive multicast traffic to only the requesters; it supports 2000 multicast groups (in C1300 1 Gigabit Ethernet SKUs) and 4000 multicast groups (in C1300 10 Gigabit Ethernet SKUs and C1300X SKUs)
● Source-specific multicasting is also supported |
| Layer 2 switching |
IGMP querier
IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router |
| Layer 2 switching |
IGMP proxy
The IGMP proxy provides a mechanism for multicast forwarding based on IGMP membership information without the need for more complicated multicast routing protocols |
| Layer 2 switching |
Head-of-Line (HOL) blocking
HOL blocking prevention |
| Layer 2 switching |
Loopback detection
Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP |
| Layer 3 |
IPv4 routing. Wire-speed routing of IPv4 packets: Up to 7168 (Dynamic + Static) IPv4 routes and up to 256 IP interfaces in C1300 10 Gigabit Ethernet SKUs and C1300X SKUs |
| Layer 3 |
IPv6 routing
Wire-speed routing of IPv6 packets |
| Layer 3 |
Layer 3 interface
Configuration of a Layer 3 interface on a physical port, LAG, VLAN interface, or loopback interface |
| Layer 3 |
Classless Interdomain Routing (CIDR)
Support for CIDR |
| Layer 3 |
Routing Information Protocol (RIP) v2
Support for RIP v2 for dynamic routing |
| Layer 3 |
Policy-Based Routing (PBR)
Flexible routing control to direct packets to a different next hop based on an IPv4 or IPv6 Access Control List (ACL) |
| Layer 3 |
Open Shortest Path First (OSPF)
Support for OSPF v2 and v3 |
| Layer 3 |
DHCP server
● Switch functions as an IPv4 DHCP server, serving IP addresses for multiple DHCP pools or scopes
● Support for DHCP options |
| Layer 3 |
DHCP relay at Layer 3
Relay of DHCP traffic across IP domains |
| Layer 3 |
User Datagram Protocol (UDP) relay
Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BOOTP)/DHCP packets |
| Stacking |
Hardware stacking
PIDs from the same Family can be stacked together. Cross-stacking between Families is not supported.
C1300X Family: C1300X-24T-4X, C1300X-24P-4X, C1300X-48T-4X, C1300X-48P-4X, C1300X-10NU-2X, C1300X-24NGU-4X, C1300X-24MU-4X, C1300X-48NGU-4X |
| Stacking |
High availability
Fast stack failover delivers minimal traffic loss. Support for LAG across multiple units in a stack |
| Stacking |
Plug-and-play stacking configuration/management
● Active/standby for resilient stack control
● Auto-numbering
● Hot swap of units in stack
● Ring and chain stacking options, auto stacking port speed, flexible stacking port options |
| Stacking |
High-speed stack interconnects
Cost-effective high-speed 10 Gigabit Ethernet fiber interfaces |
| Security |
Secure Shell (SSH) Protocol
● SSH is a secure replacement for Telnet traffic. Secure Copy Protocol (SCP) also uses SSH.
● SSH v1 and v2 are supported |
| Security |
Secure Sockets Layer (SSL)
SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch |
| Security |
IEEE 802.1X (authenticator role)
● 802.1X: RADIUS authentication and accounting, MD5 hash, guest VLAN, unauthenticated VLAN, single/multiple host mode, and single/multiple sessions
● Supports time-based 802.1X, dynamic VLAN assignment, and MAC authentication |
| Security |
IEEE 802.1X supplicant
A switch can be configured to act as a supplicant to another switch. This enables extended secure access in areas outside the wiring closet (such as conference rooms) |
| Security |
Web-based authentication
Web-based authentication provides network admission control through a web browser to any host devices and operating systems |
| Security |
STP Bridge Protocol Data Unit (BPDU) Guard
A security mechanism to protect the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. This avoids accidental topology loops |
| Security |
STP Root Guard
Prevents edge devices not in the network administrator’s control from becoming STP root nodes |
| Security |
STP loopback guard
Provides additional protection against Layer 2 forwarding loops (STP loops) |
| Security |
DHCP snooping
Filters out DHCP messages with unregistered IP addresses and/or from unexpected or untrusted interfaces. This prevents rogue devices from behaving as DHCP servers |
| Security |
IP Source Guard (IPSG)
When IPSG is enabled at a port, the switch filters out IP packets received from the port if the source IP addresses of the packets have not been statically configured or dynamically learned from DHCP snooping. This prevents IP address spoofing |
| Security |
IP Source Guard (IPSG)
When IPSG is enabled at a port, the switch filters out IP packets received from the port if the source IP addresses of the packets have not been statically configured or dynamically learned from DHCP snooping. This prevents IP address spoofing |
| Security |
Dynamic ARP Inspection (DAI)
● The switch discards ARP packets from a port if there are no static or dynamic IP/MAC bindings or if there is a discrepancy between the source or destination addresses in the ARP packet
● This prevents man-in-the-middle attacks |
| Security |
IP/MAC/port binding (IPMB)
The preceding features (DHCP snooping, IP Source Guard, and Dynamic ARP Inspection) work together to prevent Denial of-Service (DoS) attacks in the network, thereby increasing network availability |
| Security |
Secure Core Technology (SCT)
Makes sure that the switch will receive and process management and protocol traffic no matter how much traffic is received |
| Security |
Secure Sensitive Data (SSD)
A mechanism to manage sensitive data (such as passwords, keys, and so on) securely on the switch, populating this data to other devices and a secure auto-configuration. Access to view the sensitive data as plain text or encrypted is provided according to the user configured access level and the access method of the user |
| Security |
Trustworthy systems
● Trustworthy systems provide a highly secure foundation for Cisco products
● Run-time defenses (Executable Space Protection [X-Space], Address Space Layout
● Randomization [ASLR], Built-In Object Size Checking [BOSC]) |
| Security |
Private VLAN
Provides security and isolation between switch ports, which helps ensure that users cannot snoop on other users’ traffic; supports multiple uplinks. |
| Security |
Layer 2 isolation Private VLAN Edge (PVE)
PVE (also known as protected ports) provides Layer 2 isolation between devices in the same VLAN; supports multiple uplinks |
| Security |
Port security
Ability to lock source MAC addresses to ports and limit the number of learned MAC addresses |
| Security |
RADIUS/TACACS+
Supports RADIUS and TACACS authentication. Switch functions as a client |
| Security |
RADIUS accounting
The RADIUS accounting functions allow data to be sent at the start and end of services indicating the number of resources (such as time, packets, bytes, and so on) used during the session |
| Security |
Storm control
Broadcast, multicast, and unknown unicast |
| Security |
DoS prevention
DoS attack prevention |
| Security |
Multiple user privilege levels in CLI
Level 1, 7, and 15 privilege levels |
| Security |
ACLs
● Support for up to 3072 rules (in Catalyst 1300X SKUs) Drop or rate limit based on source and destination MAC, VLAN ID, IPv4 or IPv6 address, IPv6 flow label, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, TCP/UDP source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, IGMP packets, TCP flag; ACL can be applied on both ingress and egress sides
● Time-based ACLs supported |
| Quality of service |
Priority levels
8 hardware queues |
| Quality of service |
Scheduling
Strict priority and Weighted Round-Robin (WRR) |
| Quality of service |
Class of service
● Port-based, 802.1p VLAN priority-based, IPv4/IPv6 IP precedence/Type of Service (ToS)/DSCP-based, Differentiated Services (DiffServ), classification and remarking ACLs, trusted QoS
● Queue assignment based on DSCP and Class of Service (802.1p/CoS) |
| Quality of service |
Rate limiting
Ingress policer; egress shaping and rate control per VLAN, per port, and flow based; dualrate 3-color (2R3C) policing |
| Quality of service |
Congestion avoidance
A TCP congestion avoidance algorithm is required to minimize and prevent global TCP loss synchronization |
| Quality of service |
iSCSI traffic optimization
A mechanism for giving priority to iSCSI traffic over other types of traffic |
| Standards |
Standards
IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad Link Aggregation Control Protocol, IEEE 802.3z Gigabit Ethernet, IEEE 802.3ae 10 Gbps Ethernet over fiber for LAN, IEEE 802.3an 10GBASE-T 10 Gbps Ethernet over copper twisted pair cable, IEEE 802.3x Flow Control, IEEE 802.1D (STP, GARP, and GVRP), IEEE 802.1Q/p VLAN, IEEE 802.1w Rapid STP, IEEE 802.1s Multiple STP; IEEE 802.1X Port Access Authentication; IEEE 802.3af; IEEE 802.3at; IEEE 802.1AB Link Layer Discovery Protocol; IEEE 802.3az Energy Efficient Ethernet; RFC 768; RFC 783; RFC 791; RFC 792; RFC 793; RFC 813; RFC 826; RFC 879; RFC 896; RFC 854; RFC 855; RFC 856; RFC 858; RFC 894; RFC 919; RFC 920; RFC 922; RFC 950; RFC 951; RFC 1042; RFC 1071; RFC 1123; RFC 1141; RFC 1155; RFC 1157; RFC 1213; RFC 1215; RFC 1286; RFC 1350; RFC 1442; RFC 1451; RFC 1493; RFC 1533; RFC 1541; RFC 1542; RFC 1573; RFC 1624; RFC 1643; RFC 1700; RFC 1757; RFC 1867; RFC 1907; RFC 2011; RFC 2012; RFC 2013; RFC 2030; RFC 2131; RFC 2132; RFC 2233; RFC 2576; RFC 2616; RFC 2618; RFC 2665; RFC 2666; RFC 2674; RFC 2737; RFC 2819; RFC 2863; RFC 3164; RFC 3176; RFC 3411; RFC 3412; RFC 3413; RFC 3414; RFC 3415; RFC 3416; RFC 4330 |
| IPv6 |
IPv6
● IPv6 host mode, IPv6 over Ethernet, dual IPv6/IPv4 stack
● IPv6 neighbor and router discovery (ND), IPv6 stateless address auto-configuration, path Maximum Transmission Unit (MTU) discovery
● Duplicate Address Detection (DAD), ICMP version 6 DHCPv6 stateful client
● IPv6 over IPv4 network with Intrasite Automatic Tunnel Addressing Protocol (ISATAP) tunnel support |
| IPv6 |
IPv6 QoS
Prioritize IPv6 packets in hardware |
| IPv6 |
IPv6 ACL
Drop or rate-limit IPv6 packets in hardware |
| IPv6 |
IPv6 First Hop Security
● RA guard
● ND inspection DHCPv6 guard
● Neighbor binding table (snooping and static entries)
● Neighbor binding integrity check |
| IPv6 |
Multicast Listener Discovery (MLD v1/2) snooping
Deliver IPv6 multicast packets only to the required receivers |
| IPv6 |
MLD proxy
The MLD proxy provides a mechanism for multicast forwarding based on MLD membership information without the need for more complicated multicast routing protocols |
| IPv6 |
IPv6 applications
Web/SSL, Telnet server/SSH, ping, traceroute, Simple Network Time Protocol (SNTP), Trivial File Transfer Protocol (TFTP), SNMP, RADIUS, syslog, DNS client, Telnet client, DHCP client, DHCP auto-config, IPv6 DHCP relay, TACACS+ |
| IPv6 |
IPv6 RFCs supported
● RFC 4443 (which obsoletes RFC 2463): ICMP version 6
● RFC 4291 (which obsoletes RFC 3513): IPv6 address architecture RFC 4291: IPv6 addressing architecture
● RFC 2460: IPv6 specification
● RFC 4861 (which obsoletes RFC 2461): neighbor discovery for IPv6
● RFC 4862 (which obsoletes RFC 2462): IPv6 stateless address auto-configuration RFC 1981: path MTU discovery
● RFC 4007: IPv6 scoped address architecture RFC 3484: default address selection mechanism
● RFC 5214 (which obsoletes RFC 4214): ISATAP tunneling
● RFC 4293: MIB IPv6: textual conventions and general group RFC 3595: textual conventions for IPv6 flow label |
| Management |
Cisco Business Dashboard
Support for embedded probe for Cisco Business Dashboard running on the switch. Eliminates the need to set up a separate hardware or virtual machine for the Cisco Business Dashboard probe onsite |
| Management |
Cisco Business mobile app
Mobile app for Cisco Business switch and wireless products. Helps to set up a local network in minutes and provide easy management at your fingertips |
| Management |
Cisco Network Plug and Play (PnP) agent
● The Cisco Network PnP solution provides a simple, secure, unified, and integrated offering to ease new branch or campus device rollouts or for provisioning updates to an existing network.
● The solution provides a unified approach to provision Cisco routers, switches, and wireless devices with a near-zero-touch deployment experience.
● Supports Cisco PnP Connect |
| Management |
Web user interface
● Built-in switch configuration utility for easy browser-based device configuration (HTTP/HTTPS)
● Supports configuration, wizards, system dashboard, system maintenance, and monitoring Basic and advanced mode for maximum operational efficiency |
| Management |
SNMP
SNMP versions 1, 2c, and 3 with support for traps, and SNMP v3 User-Based Security Model (USM) |
| Management |
Standard MIBs
lldp-MIB; lldpextdot1-MIB; lldpextdot3-MIB; lldpextmed-MIB; rfc2674-MIB; rfc2575-MIB; rfc2573-MIB; rfc2233-MIB; rfc2013-MIB; rfc2012-MIB; rfc2011-MIB; RFC-1212; RFC-1215; SNMPv2-CONF; SNMPv2-TC; p-bridge-MIB; rfc2668-MIB; rfc2737-MIB; rfc2925-MIB; rfc3621-MIB; rfc4668-MIB; rfc4670-MIB; trunk-MIB; tunnel-MIB; udp-MIB; draft-ietf-bridge-8021x-MIB; draft-ietf-bridge-rstpmib-04-MIB; draft-ietf-hubmib-etherif-mib-v3-00-MIB; draft-ietf-syslog-device-MIB; ianaaddrfamnumbers-MIB; ianaifty-MIB; ianaprot-MIB; q-bridge-MIB; rfc1389-MIB; rfc1493-MIB; rfc1611-MIB; rfc1612-MIB; rfc1850-MIB; rfc1907-MIB; rfc2571-MIB; rfc2572-MIB; rfc2574-MIB; rfc2576-MIB; rfc2613-MIB; rfc2665-MIB; inet-address-MIB; ip-forward-MIB; ip-MIB; RFC1155-SMI; RFC1213-MIB; SNMPv2-MIB; SNMPv2-SMI; SNMPv2-TM; RMON-MIB; rfc1724-MIB; dcb-raj-DCBX-MIB-1108-MIB; rfc1213-MIB; rfc1757-MIB |
| Management |
Private MIBs
CISCOSB-lldp-MIB; CISCOSB-brgmulticast-MIB; CISCOSB-bridgemibobjects-MIB; CISCOSB-bonjour-MIB; CISCOSB-dhcpcl-MIB; CISCOSB-MIB; CISCOSB-wrandomtaildrop-MIB; CISCOSB-traceroute-MIB; CISCOSB-telnet-MIB; CISCOSB-stormctrl-MIB; CISCOSBssh-MIB; CISCOSB-socket-MIB; CISCOSB-sntp-MIB; CISCOSB-smon-MIB; CISCOSB-phy-MIB; CISCOSB-multisessionterminal-MIB; CISCOSB-mri-MIB; CISCOSB-jumboframes-MIB; CISCOSB-gvrp-MIB; CISCOSB-endofmib-MIB; CISCOSB-dot1x-MIB; CISCOSB-deviceparams-MIB; CISCOSB-cli-MIB; CISCOSB-cdb-MIB; CISCOSB-ip-MIB; CISCOSB-iprouter-MIB; CISCOSB-ipv6-MIB; CISCOSB-mnginf-MIB; CISCOSB-lcli-MIB; CISCOSB-localization-MIB; CISCOSB-mcmngr-MIB; CISCOSB-mng-MIB; CISCOSB-physdescription-MIB; CISCOSB-PoE-MIB; CISCOSB-protectedport-MIB; CISCOSB-rmon-MIB; CISCOSB-rs232-MIB; CISCOSB-SecuritySuite-MIB; CISCOSB-snmp-MIB; CISCOSB-specialbpdu-MIB; CISCOSB-banner-MIB; CISCOSB-syslog-MIB; CISCOSB-TcpSession-MIB; CISCOSB-traps-MIB; CISCOSB-trunk-MIB; CISCOSB-tuning-MIB; CISCOSB-tunnel-MIB; CISCOSB-udp-MIB; CISCOSB-brgmacswitch-MIB; CISCOSB-3sw2swtables-MIB; CISCOSB-smartPorts-MIB; CISCOSB-tbi-MIB; CISCOSB-macbaseprio-MIB; CISCOSB-env_mib-MIB; CISCOSB-policy-MIB; CISCOSB-sensor-MIB; CISCOSB-aaa-MIB; CISCOSB-application-MIB; CISCOSB-bridgesecurity-MIB; CISCOSB-copy-MIB; CISCOSB-CpuCounters-MIB; CISCOSB-Custom1BonjourService-MIB; CISCOSB-dhcp-MIB; CISCOSB-dlf-MIB; CISCOSB-dnscl-MIB; CISCOSB-embweb-MIB; CISCOSB-fft-MIB; CISCOSB-file-MIB; CISCOSB-greeneth-MIB; CISCOSB-interfaces-MIB; CISCOSB-interfaces_recovery-MIB; CISCOSB-vlan-MIB; CISCOSB-ipstdacl-MIB; CISCOSB-eee-MIB; CISCOSB-ssl-MIB; CISCOSB-qosclimib-MIB; CISCOSB-digitalkeymanage-MIB; CISCOSB-tbp-MIB; CISCOSMB-MIB; CISCOSB-secsd-MIB; CISCOSB-draft-ietf-entmib-sensor-MIB; CISCOSB-draft-ietf-syslog-device-MIB; CISCOSB-rfc2925-MIB; CISCO-SMI-MIB; CISCOSB-DebugCapabilities-MIB; CISCOSB-CDP-MIB; CISCOSB-vlanVoice-MIB; CISCOSB-EVENTS-MIB; CISCOSB-sysmng-MIB; CISCOSB-sct-MIB; CISCO-TC-MIB; CISCO-VTP-MIB; CISCO-CDP-MIB |
| Management |
Remote Monitoring (RMON)
Embedded RMON software agent supports 4 RMON groups (history, statistics, alarms, and events) for enhanced traffic management, monitoring, and analysis |
| Management |
IPv4 and IPv6 dual stack
Coexistence of both protocol stacks to ease migration |
| Management |
Firmware upgrade
● Web browser upgrade (HTTP/HTTPS) and TFTP and upgrade over SCP running over SSH
● Dual images for resilient firmware upgrades |
| Management |
Port mirroring
Traffic on a port can be mirrored to another port for analysis with a network analyzer or RMON probe. Up to 8 source ports can be mirrored to one destination port |
| Management |
VLAN mirroring
Traffic from a VLAN can be mirrored to a port for analysis with a network analyzer or RMON probe. Up to 8 source VLANs can be mirrored to one destination port |
| Management |
Flow-based redirection and mirroring
Redirect or mirror traffic to a destination port or mirroring session based on flow |
| Management |
Remote Switch Port Analyzer (RSPAN)
Traffic can be mirrored across a Layer 2 domain to a remote port on a different switch for easier troubleshooting |
| Management |
sFlow agent
Switch can export sFlow sample to external collectors. sFlow provides visibility into network traffic down to the flow level |
| Management |
DHCP (options 12, 59, 60, 66, 67, 82, 125, 129, and 150)
DHCP options facilitate tighter control from a central point (DHCP server) to obtain IP address, auto-configuration (with configuration and image file download), DHCP relay, and hostname |
| Management |
Secure Copy (SCP)
Securely transfer files to and from the switch |
| Management |
Auto-configuration with SCP file download
Enables secure mass deployment with protection of sensitive data |
| Management |
Text-editable configuration files
Configuration files can be edited with a text editor and downloaded to another switch, facilitating easier mass deployment |
| Management |
Smartports
Simplified configuration of QoS and security capabilities |
| Management |
Auto Smartports
● Applies the intelligence delivered through the Smartport roles and applies it automatically to the port based on the devices discovered over Cisco Discovery Protocol or LLDP-MED.
● This facilitates zero-touch deployments |
| Management |
Text view CLI
Scriptable CLI. A full CLI as well as a menu-based CLI is supported. User privilege levels 1, 7, and 15 are supported for the CLI |
| Management |
Localization
Localization of GUI and documentation into multiple languages |
| Management |
Login banner
Configurable multiple banners for web as well as CLI |
| Management |
Other management
Traceroute, single IP management, HTTP/HTTPS, SSH, RADIUS, port mirroring, TFTP upgrade, DHCP client, BOOTP, SNTP, Xmodem upgrade, cable diagnostics, ping, syslog, Telnet client (SSH secure support), automatic time settings from management station |
| Green (power efficiency) |
Energy detect
Automatically turns power off on an RJ-45 port when the detecting link down. Active mode is resumed without loss of any packets when the switch detects the link is up |
| Green (power efficiency) |
Cable length detection
Adjusts the signal strength based on the cable length. Reduces the power consumption for shorter cables |
| Green (power efficiency) |
IEEE compliant (802.3az)
Supports IEEE 802.3az on all copper Gigabit Ethernet ports |
| Green (power efficiency) |
Disable port LEDs
LEDs can be manually turned off to save energy |
| Green (power efficiency) |
Time-based port operation
Link up or down based on user-defined schedule (when the port is administratively up) |
| Green (power efficiency) |
Time-based PoE
PoE power can be on or off based on a user-defined schedule to save energy |
| Green (power efficiency) |
Persistent PoE
Provides PoE power while the device is rebooting |
| General |
Jumbo frames
Frame sizes up to 9000 bytes. The default MTU is 2000 bytes |
| General |
MAC table
Up to 32,000 rules |
| General |
Chip guard
Detects tampering attempts and responds during bootup |
| General |
Boot integrity
Boot integrity visibility allows Cisco’s platform identity and software integrity information to be visible and actionable |
| Discovery |
Bonjour
The switch advertises itself using the Bonjour protocol |
| Discovery |
Link Layer Discovery Protocol (LLDP) (802.1ab) with LLDPMedia Endpoint Discovery (MED) extensions
LLDP allows the switch to advertise its identification, configuration, and capabilities to neighboring devices that store the data in a MIB. LLDP-MED is an enhancement to LLDP that adds the extensions needed for IP phones |
| Discovery |
Cisco Discovery Protocol
The switch advertises itself using the Cisco Discovery Protocol. It also learns the connected device and its characteristics via Cisco Discovery Protocol |
| Power over Ethernet (PoE) |
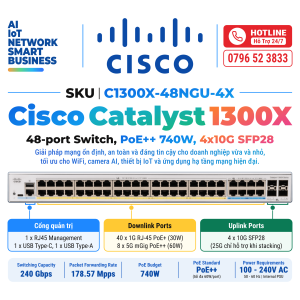
The following switches support 802.3bt (Type 3) PoE++ and 802.3at PoE+. The total power available for PoE per switch is as follows:
● Power dedicated to PoE: 740W;
● Number of ports that support PoE: 24 |
| Hardware |
Power consumption (worst case)
● System power consumption: 110V = 104.2W, 220V = 103.9W;
● Power consumption (with PoE): 110V = 909.8W, 220V = 870.8W;
● Heat dissipation: 3104.3 BTU/hr;
● Idle power: 110V = 25.5W, 220V = 26.8W |
| Hardware |
Ports
● Total system Ports: 16 x Gigabit Ethernet + 8 x 5G mGig + 4 x 10G;
● Downlink Ports: 16 x 1G + 8 x 5G mGig;
● Uplink Ports: 4 x 10G SFP28 (10G Uplink, 25G available for stacking only) |
| Hardware |
Console port
Cisco standard RJ-45 console port and USB Type C port |
| Hardware |
USB port
USB Type C port on the front panel of the switch for easy file and image management as well as console port |
| Hardware |
Buttons
Reset button |
| Hardware |
Cabling type
Unshielded Twisted Pair (UTP) Category 5e or better for 1000BASE-T |
| Hardware |
LEDs
System, Link/Act, PoE, Speed |
| Hardware |
Flash
1GB SLC |
| Hardware |
CPU
ARM dual-core at 1.5 GHz |
| Hardware |
DRAM
2 GB DDR4 (C1300X) |
| Hardware |
Packet buffer
All numbers are aggregate across all ports, as the buffers are dynamically shared: 3 MB |
| Hardware |
Supported SFP modules. Tra cứu tại:
https://tmgmatrix.cisco.com/ |
| Environmental |
Unit dimensions (W x D x H)
444.3 x 270 x 43.94 mm (17.49 x 10.63 x 1.73 in) |
| Environmental |
Unit weight
4.23kg (9.33lb) |
| Environmental |
Power
100-240V 50-60 Hz, internal, universal |
| Environmental |
Certifications
UL (UL 62368), CSA (CSA 22.2), CE mark, FCC Part 15 (CFR 47) Class A |
| Environmental |
Operating temperature. Minimum ambient temperature for cold start is 32°F (0°C)
23° to 122°F (-5° to 50°C) |
| Environmental |
Storage temperature
-13° to 158°F (-25° to 70°C) |
| Environmental |
Operating humidity
10% to 90%, relative, noncondensing |
| Environmental |
Storage humidity
10% to 90%, relative, noncondensing |
| Environmental |
Acoustic noise and mean time between failures (MTBF)
● Fan (number): 1;
● Acoustic noise: 25°C: 49.5 dBA;
● MTBF at 25°C (hours): 343,272 |
| Environmental |
Warranty
≥ 1 years |
| Package contents |
● Cisco Catalyst 1300X Series Switch
● Power cord included (power adapter for select 8-port SKUs), unless ‘NO-POWER-CORD’ is selected while ordering
● Mounting kit (Only 24-and 48-port models include the 19-in mounting brackets with the switch)
● Pointer card |
| Minimum requirements |
● Web browser: Chrome, Firefox, Edge, Safari
● Category 5e Ethernet network cable
● TCP/IP, network adapter, and network operating system (such as Microsoft Windows, Linux, or Mac OS X) installed |
| Accessories |
● CAB-CONSOLE-RJ45 (Console cable 6 feet with RJ-45)
● CAB-CONSOLE-USB-C (Console cable USB-C type)
● CAB-CONSOLE-USB-C= (Console cable USB-C type) |
| Accessories |
Cisco rack-mounting kit
RCKMNT-1RU-1K= (Rack-mount kit for 1 RU for C1000, C1200, C1300)
Chỉ các model 24 cổng và 48 cổng mới được tặng kèm sẵn tai gắn rack 19 inch (19-in. mounting brackets). Các model có ít cổng hơn (ví dụ 8 cổng, 12 cổng, 16 cổng) không có tai rack trong hộp. |
| For more information |
To find out more about the Cisco Catalyst 1300 Series Switches, Visit
https://www.cisco.com/c/en/us/products/switches/catalyst-1300-series-switches/index.html |
 Router – Cân Bằng Tải
 Switch – Bộ Chuyển Mạch
 Module Quang & Cáp
 Power & PoE
 Wifi – Chuyên Dụng | Diện Rộng
 Firewall – Tường Lửa
 Server – Máy Chủ
 NAS – Thiết Bị Lưu Trữ
 Ổ Cứng Chuyên Dụng
 Tổng Đài IP (PBX)
 Điện Thoại IP
 Hội Nghị Truyền Hình
 Phần Mềm
 Smart Office AI
 Smart Home AI
 Cho Thuê Thiết Bị Mạng
 Hàng Like New – Hàng Cũ – Thanh Lý
Đánh giá
Chưa có đánh giá nào.